Insights & Resources
Expert perspectives on data protection, compliance, and cybersecurity.
Why Traditional Security Stops Working After Data Leaves Your Organization
Explore why perimeter-based security fails once data is shared externally, and how persistent data protection fills the gap.
Persistent Data Protection vs Traditional DLP
A deep dive comparing traditional Data Loss Prevention with modern persistent data protection approaches.
8 min read
How to Revoke Access to a Shared Document
Step-by-step guide on maintaining control over shared documents and revoking access when needed.
5 min read
Blockchain and Tamper-Proof Audit Trails
How blockchain technology enables tamper-proof audit trails for enterprise data protection and compliance.
7 min read
Securing Digital Inheritance and Sensitive Transfers
The growing importance of securing digital assets and how time-locked capsules enable safe digital inheritance.
6 min read
The Data You Don't Know You Have
Most organizations can't answer where their sensitive data lives. Why manual review fails at scale, and what changes when discovery is automated.
5 min read
Standard, Custom, or Free Language: Three Ways to Classify What Matters
Single-mode classification misses what doesn't fit the pattern. How three classification layers — standard, custom, and free-language — work together.
6 min read
You Found 200,000 Sensitive Files. Now What?
Discovery without prioritization just relocates the anxiety. How risk scoring turns a flat list of findings into a clear order of operations.
5 min read
What an AI Agent Finds That Pattern Matching Misses
Rules catch structured data and miss everything else. How intent-based detection via an AI Agent reaches the unstructured content that matters most.
6 min read
Before You Sign: Knowing What's in the Data You're Acquiring
In M&A you inherit a target's data — and its exposure. Why data risk deserves the same look as the financials, before you close.
5 min read
Who Accessed Your Sensitive Data in the Last Six Months?
A regulator asks who accessed customer data in the last six months. Why a continuous Audit Trail turns a logistical nightmare into an evidence-backed answer.
5 min read
The Anatomy of an Insider Threat
The most damaging incidents come from authorized people doing normal-looking things. Why insider risk is a behavior problem, not a perimeter problem.
5 min read
Five Access Patterns That Should Never Go Unnoticed
Anomaly detection named: five access patterns — volume spikes, odd hours, first contact, outward movement, broken baselines — that should never go unnoticed.
6 min read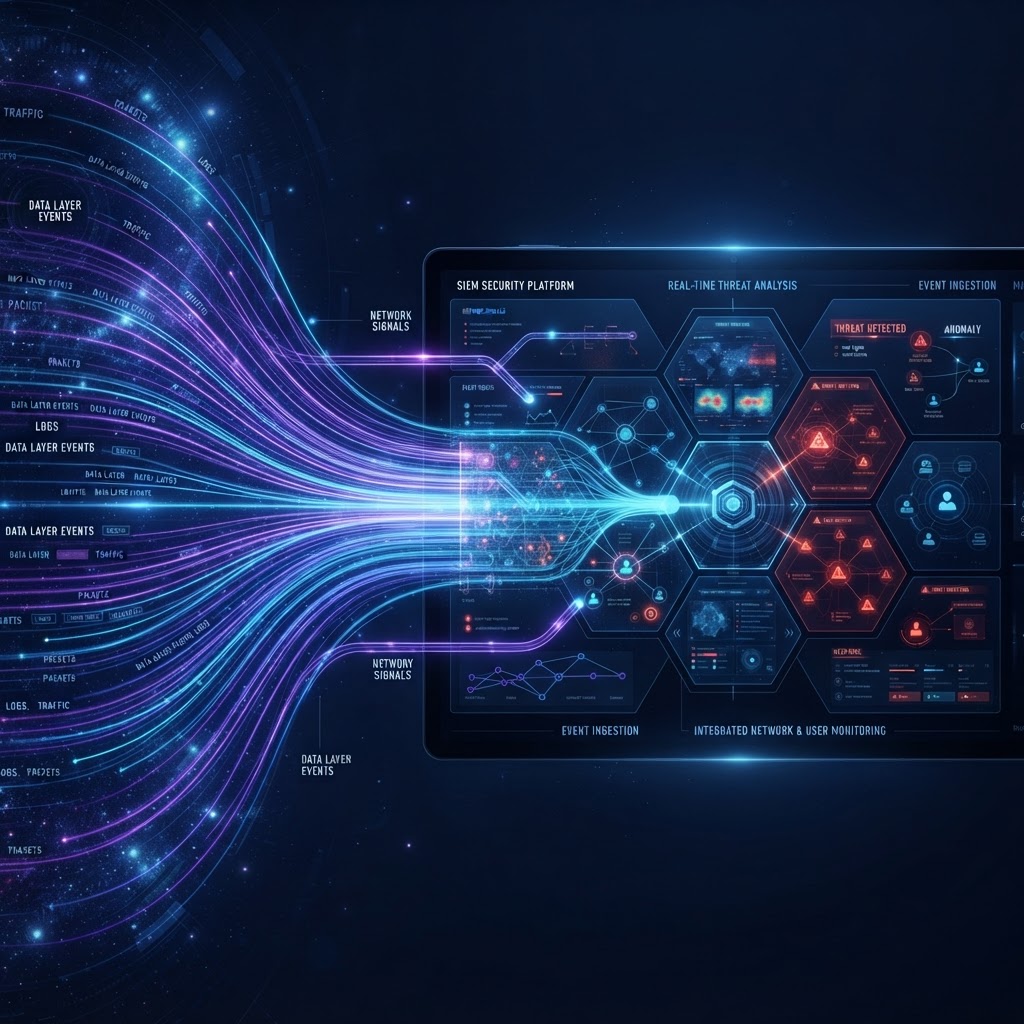
From Audit Trail to SIEM: Closing the Data Blind Spot
The SOC sees networks, endpoints, and identities but not the data itself. How feeding the data layer into your SIEM closes the blind spot.
5 min read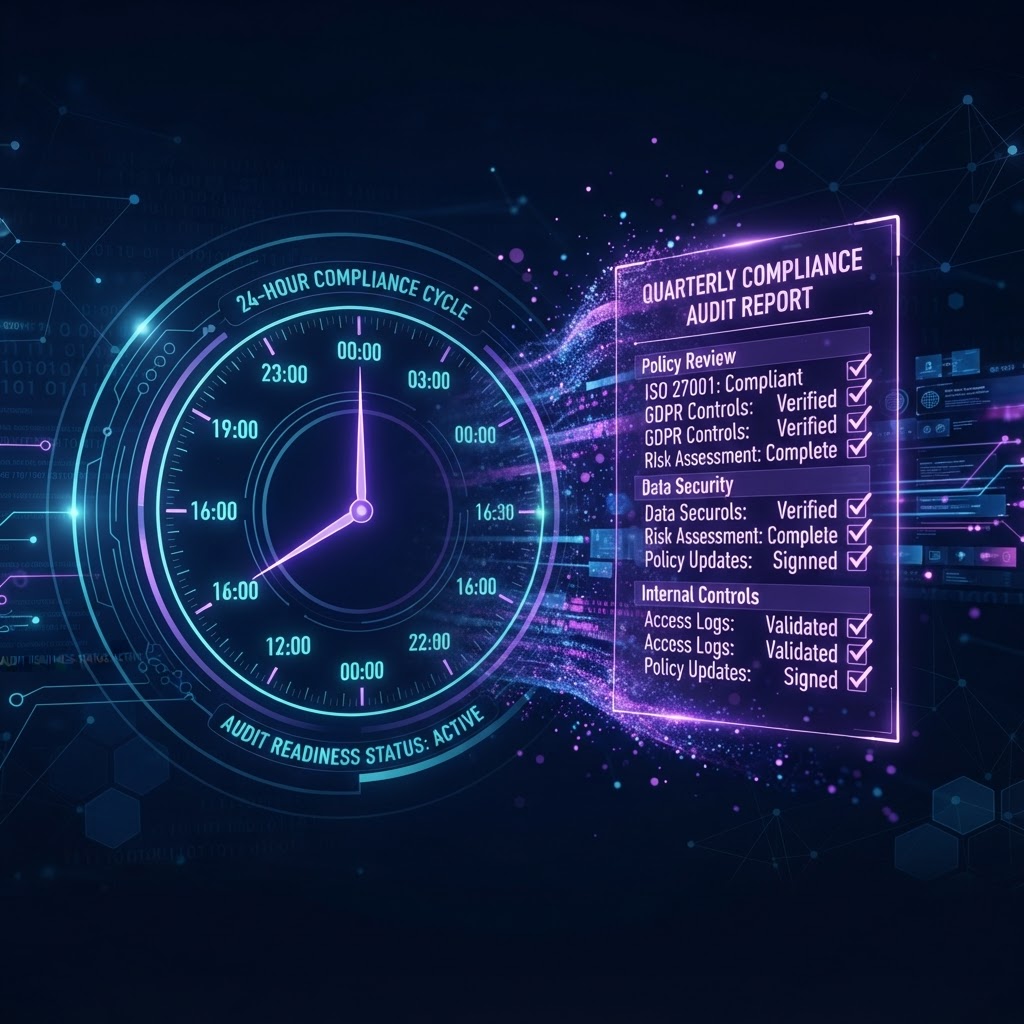
Audit-Ready in 24 Hours, Not Three Weeks
When an audit request lands, the clock starts. How a continuous Audit Trail turns weeks of scrambling into a query.
5 min read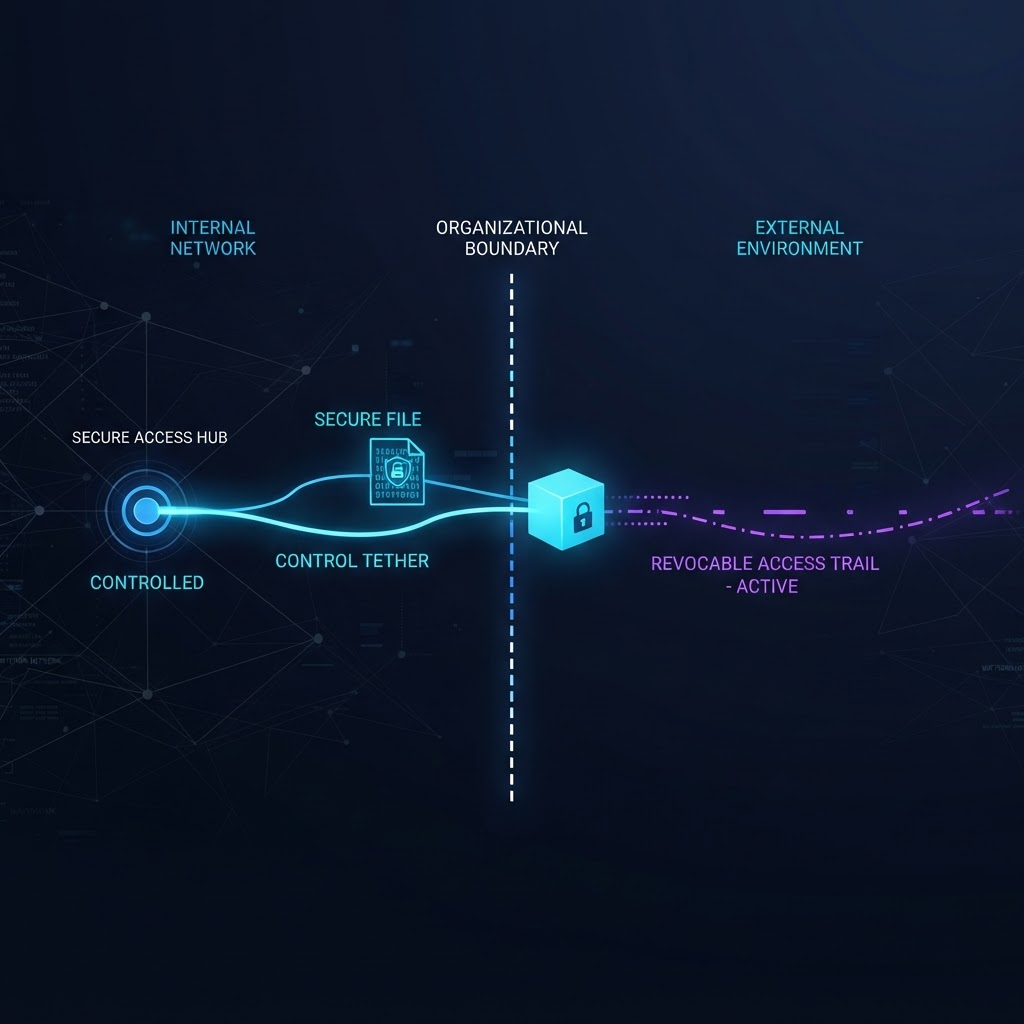
What Happens to a File After It Leaves Your Organization?
The moment a file leaves your organization, visibility ends. How control that travels with the file closes the blind spot where most leaks happen.
5 min read
The Email Attachment Is the Problem
An attachment is a copy you can't recall. How replacing uncontrolled copies with revocable, logged, time-limited links changes external sharing.
5 min read
Collaborate With the Outside World Without Giving It Away
External collaboration usually ends data control. How co-editing on your own storage with revocable access keeps the business moving without leaks.
5 min read
Every File You Receive Is Something You Didn't Choose
Organizations protect outbound data and ignore what arrives. Why inbound files deserve the same scanning before they land inside your environment.
5 min read
Strong Protection Without Moving a Single File
Real protection shouldn't require a migration. How applying a secure vault and encryption over existing storage removes the biggest reason projects stall.
5 min read